Enterprise trust, built into the platform
Nevado helps regulated organizations build and operate governed software and AI applications with security, governance, auditability, human oversight, and clear ownership built in from the start.
Build trust into every layer
Security and compliance are part of the operating model from the beginning—across workflow design, model selection, review, deployment, and ongoing change.
Scoped work
Engagements start with defined owners, boundaries, and accountability.
AI-accelerated build
Applications are produced faster with AI working inside the governed flow.
Human review and approval
Nothing ships without explicit sign-off at defined review points.
Traceable record
Activity and decisions are captured in an audit trail — attributable and reviewable.
Operated with oversight
Running applications stay governed as they change and grow.
Model selection is a governed decision
The model behind each workflow is a deliberate choice — made per use case instead of forcing everything through one provider — and weighed against the same criteria every time.
- Task fit
- Data sensitivity
- Performance
- Risk
- Compliance
- Cost
Keep your operating model. Evolve your trust layer
Nevado works within your environment while defining what stays under your control. Responsibilities are mapped explicitly for every deployment — so there's no ambiguity about who owns what as your applications evolve.
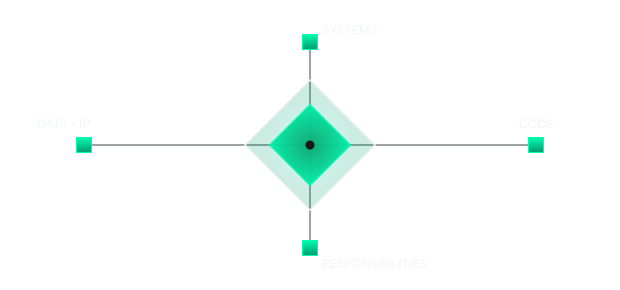
- Defined together, per deployment
- Infrastructure responsibilities
- Deployment
- Maintenance
- Ongoing application changes
The trust layer keeps evolving
Nevado is SOC 2 Type II audited, with controls independently validated over time. It's one piece of a larger compliance program — built with each client and maintained long after launch.
-
SOC 2 Type II
A verified proof point within the broader compliance program.
-
Controls tailored to your environment
Access, review, documentation, and governance requirements are shaped around your workflows, policies, and operating environment.
-
Per-deployment governance
Governance and documentation requirements are defined for every deployment before it goes live.
-
Ongoing oversight
Oversight continues as applications and requirements evolve — compliance doesn't stop at launch.
-
Expanding standards
Additional standards and certifications are added to the program over time.
Need a deeper security conversation?
Talk with our team about governance, ownership, compliance, and the controls surrounding your use case.
Talk to Our Team